A course by Kavis Network
Pentest SaaS withAI now.
End-to-end SaaS product and web application penetration testing, run on AI-assisted workflows. Ten hands-on phases take you from recon and exploitation to automation and professional reporting, and leave you ready to hunt bug bounties. Structured over one month, taught in Tamil.
Ten AI-assisted phases, Phase 00 to 09, plus three final capstone tracks
Finish able to run end-to-end SaaS pentests and hunt bug bounties with AI
Start anytime · structured over a month · recorded, plus a weekly live session
₹15,000 one-time (course worth ₹25,000), two years of access, 20 seats in this batch
AI won’t take your job.Someone using AI will.
The field is moving at machine speed. The people who learn to test with AI now are the ones who get hired, get ahead, and stay relevant. Wait, and you spend years chasing a gap that widens every single day. This course is built to put you on the right side of it.
The attackers already automated
Adversaries use AI to find and weaponise weaknesses in minutes. Defend by hand and you are already a step behind.
The gap compounds daily
A peer using AI does in an hour what takes you a week. Six months of that is a career’s worth of distance.
Manual skills get commoditised
Recon, triage, boilerplate reports: AI does them instantly. Hand-only work becomes the easiest to replace.
Hiring already shifted
Roles now expect AI-augmented workflows. “I don’t use AI” is fast becoming “I can’t do the job.”
You don’t need to fear AI. You need to be the one wielding it, starting today. Here’s exactly what you’ll learn to do.
Where AI plugs into offense and defense.
Phase 01 opens with the career map, because you should know what you are training for. Every security role is being rebuilt around AI. Here is where it actually lands, on both sides of the house, and where this course points you.
Break in, on purpose
Penetration Testing
AI drives recon, chains findings into attack paths and drafts the report.
SaaS & API Security
AI fuzzes endpoints and hunts BOLA, IDOR and broken auth at scale.
Bug Bounty Hunting
AI widens your attack surface and turns findings into accepted reports.
Red Teaming
AI simulates real adversaries and builds believable, end-to-end scenarios.
OSINT & Recon
AI aggregates and correlates a target’s footprint in seconds.
Hold the line
SOC & Detection
AI triages alerts, cuts the noise and surfaces the threats that matter.
IAM & Identity
AI flags anomalous access and drives adaptive, risk-based auth.
Threat Intelligence
AI digests feeds and reports to predict the next campaign.
Incident Response & DFIR
AI accelerates containment, triage and forensic timelines.
AppSec & Code Review
AI reviews every commit for vulnerabilities before release.
AI doesn’t replace the tester. It becomes your force multiplier.
The goal of this program is simple: train you to run end-to-end SaaS and web application penetration tests on AI-assisted workflows, so you work faster, go deeper, and can take that straight into bug bounty.
Every phase is AI-assisted
Phase 00 sets the mindset: what AI can and cannot do in an engagement. From there recon, exploitation and reporting all run on prompts, agents and automation.
Hands-on from day one
You build your own lab: Kali and Windows, DVWA, Metasploitable2 and a custom bank lab. Every target you attack is one you legally own.
Finish with proof
Three capstone tracks and a professional report. You leave with tooling you built, findings you can show, and a bug bounty workflow you can run.
You are starting from zero in security and want a route that does not assume a degree or a job in it already.
You already work in IT or support and want to move across into offensive security.
You can test manually but have never used AI in an engagement, and can feel the gap opening.
It is not for you if you want a certificate at the end, because this course does not issue one, or if you are looking for ready-made attack tools rather than the skill to build and use them legally.
Ten phases, mindset to bug bounty ready.
This is the whole program. Phase 00 through Phase 09, then the capstone tracks you finish on. Every phase is AI-assisted and every phase is hands-on: labs you stand up yourself, tools you actually run, and findings you write up properly. Pick one to see what is inside it.
AI-First Pentest Mindset
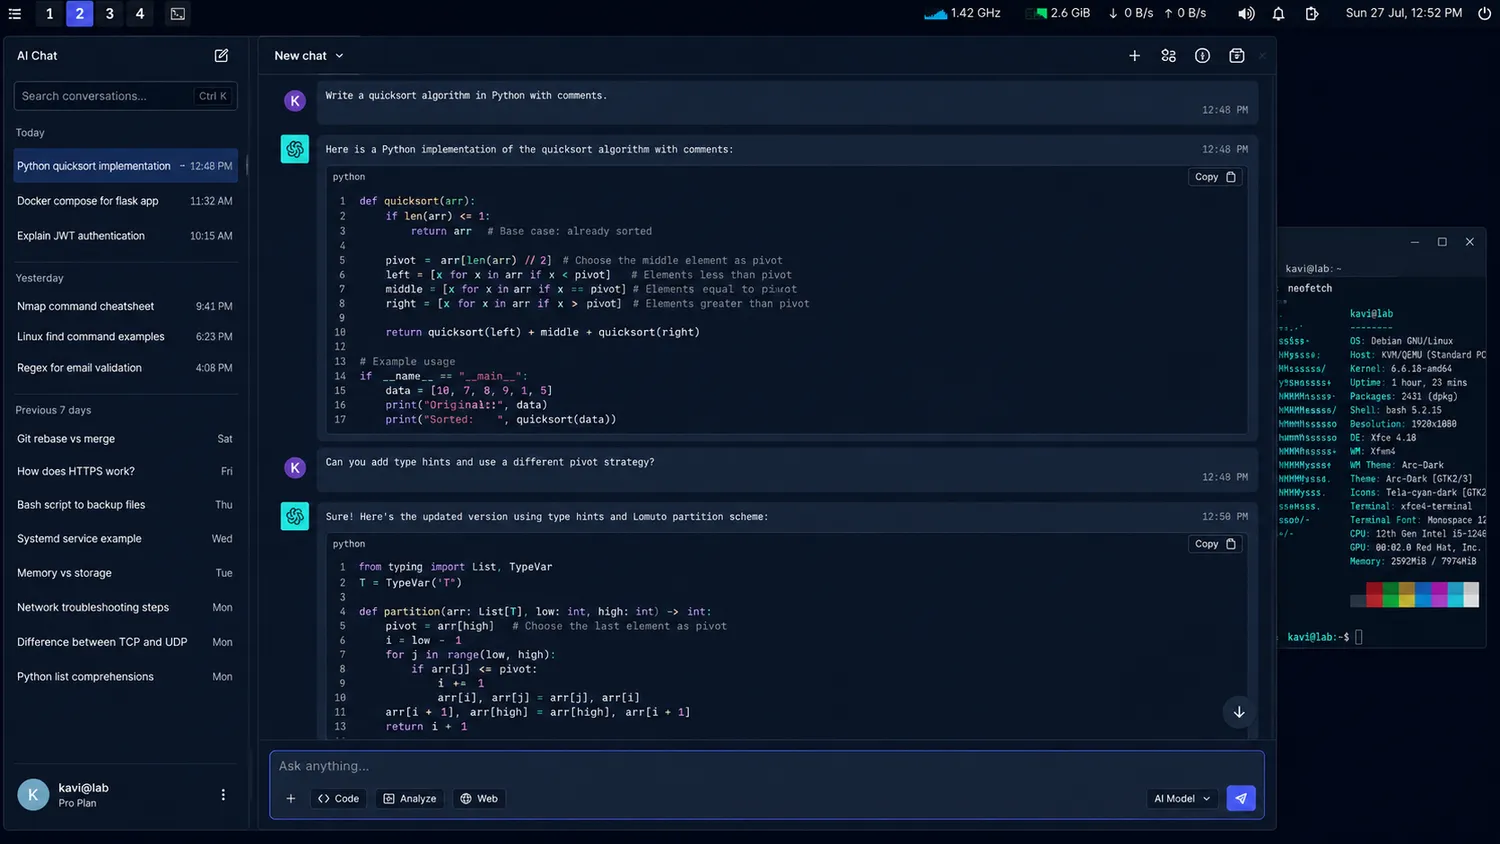
Where the program starts. What AI can and cannot do in an engagement, which model to reach for, and how to prompt it so it helps instead of hallucinates.
A model-selection and prompting playbook for security work, the habit every later phase runs on.
What you can do when you finish.
Seven concrete capabilities, not a certificate. This is the standard the program is measured against. By the end, each of these is something you have actually done, not just watched.
AI-assisted recon
Perform reconnaissance and attack surface mapping with AI doing the heavy lifting.
Exploit SaaS & web
Identify and exploit SaaS and web application vulnerabilities with AI support.
Automate the workflow
Automate penetration testing workflows end to end with AI and Python.
API & SaaS testing
Conduct API and SaaS security testing efficiently, including BOLA and IDOR at scale.
Professional reporting
Generate professional vulnerability reports, proofs of concept and remediation using AI.
Build your own tools
Build intelligent offensive security tooling instead of only running other people’s.
Bug bounty ready
Participate in bug bounty programs with AI-enhanced productivity: a real methodology, a portfolio of findings, and the tooling to keep going.
Same work, a fraction of the time.
AI-assisted phases, 00 → 09
hands-on modules
final capstone tracks
One prompt. The tools do the rest.
Prompt
You describe the target in plain English
Claude plans
Picks the recon path & the tools to run
MCP drives
Operates Burp, nmap & your custom agents
n8n verifies
URLs & IPs checked against threat intel
Report
Findings + fixes written up for you
n8n does the watching. URL and IP reputation checks (VirusTotal + AbuseIPDB) run as automated workflows in the background, so verification never waits on you. You wire these up yourself in Phase 02.
AI armed the attackersand the defenders.
Every leap that makes defense faster makes offense faster too. AI widened the attack surface and the defense surface in the same breath. You train on the offensive side here, but you need to understand both to be any good at either.
What got easier to break
The skill barrier collapsed
Working offensive tooling can now be assembled with AI in a closed lab in hours. No payload or code is shared here. The point is that the barrier has all but vanished.
Signatures stopped keeping up
AI spins out endless variants of the same threat, so matching known-bad files no longer holds the line on its own.
Flawless phishing at scale
Perfect, personalised lures in any language, written in seconds and sent to thousands.
Exploit timelines collapsed
Recon to a working proof of concept now takes a fraction of the time it used to.
What got easier to protect
AI reads everything
It triages alerts, correlates logs and surfaces anomalies no human team has the hours to chase.
Zero-day prediction
A code-review agent flags exploitable bugs before they ever ship to production.
Response at machine speed
n8n workflows verify, block and escalate automatically, without waiting on a human in the loop.
Every attack tool has a defender twin
The same models that can write malware are just as good at detecting, reversing and neutralising it.
Everything here is taught legally. Phase 01 starts with ethics, not exploits: rules of engagement, scope, NDAs and responsible disclosure. Every technique in this course is practised against targets you own or are explicitly authorised to test: your own lab, DVWA, Metasploitable2, or a bug bounty program that invited you in. Attackers already have these tools. Learning them properly is how you get paid to stop them.
One month, ten phases, ₹15,000.
One payment, no subscription, and no batch to wait for. You start the day you enrol, with recorded sessions you take at your own pace, a live doubt-clearing session every week, and the whole program taught in Tamil.
The full program: every phase from the AI-first mindset through to bug bounty workflow, plus the capstone track you finish on. Nothing gated behind a second payment. Twenty seats per batch, so the weekly live session stays small enough that your questions actually get answered.
Structured over one month
No batch to wait for. Access opens as soon as you enrol. Keeping the four-week pace takes about 10 to 12 hours a week, and taking longer is fine and common, because the recordings mean you set the speed, not the calendar.
Recorded sessions
Every session is recorded. Set your own pace and rewatch any phase as often as you need.
Weekly doubt-clearing, live
A live session every week to unblock you on labs, tooling and your own findings. Your batch fixes the day together in the community group, so it lands when you can actually attend.
Two years of access
The recordings and materials stay yours for two years, so you can come back to a phase months later when a real target needs it.
Taught in Tamil
The whole curriculum explained in Tamil, with the technical terms kept in English.
No prior security experience needed. Phase 01 starts at lab setup and OS basics.
Everything people ask before they enrol.
If something here is still unclear, message us directly. The links are just below, and we answer every one.
No. Phase 01 starts at lab setup and Windows and Linux fundamentals, and Phase 02 teaches the networking and Python you need from the ground up. If you are comfortable using a computer, you can start here. Everything after that is built on what the earlier phases gave you.
Let’s connect.
Questions before you enrol? Reach us on any of these. We answer everything about prerequisites, pace and what you finish with.
Balakavi
LEAD INSTRUCTOR · FOUNDER, KAVIS NETWORK
2,500+ subscribers on YouTube·Second batch of this course
Kavis Network is a security practice that uses AI to work faster. We drive pentests with Claude Code and MCPs, build custom API-testing and code-review agents, and automate threat detection with n8n. This course is the workflow we actually run, taught end to end: ten AI-assisted phases from lab setup to bug bounty.


